HIPAA Tracking Pixels on Medical Website: Compliance Risks
Learn how common marketing tools like tracking pixels on your medical website can lead to HIPAA violations and discover how to audit your site to protect patient data today.
Learn how to evaluate ambient clinical documentation tools to ensure patient privacy. Protect your practice with these essential HIPAA compliance steps before integrating new technology into your daily patient workflows.
Sarah Mendez
HIPAA Compliance Lead

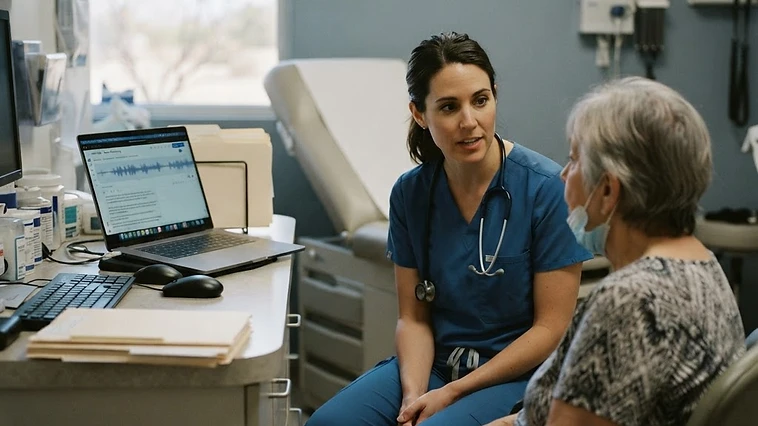
AI scribe HIPAA compliance requires that any tool processing audio recordings of patient visits meets federal standards for the transmission and storage of protected health information. Because these tools listen to conversations inside your exam rooms and translate them into clinical notes, they inherently handle sensitive patient data from the moment of activation. You must identify exactly where this data goes after the recorder stops.
Your healthcare IT consulting team should confirm whether the software provider keeps copies of raw audio files. If they do, those files count as PHI. You need to ensure the vendor maintains robust encryption both during transit to their servers and while the data sits at rest in their cloud environment.
A Business Associate Agreement is a mandatory legal contract between your practice and the software vendor. It outlines the specific responsibilities of the provider to protect PHI as defined by the Office for Civil Rights. Without a signed BAA, you cannot legally use any tool that touches patient data in your practice. You must review the specific language within this contract before starting your rollout.
Never settle for a generic click-wrap agreement found online during software registration. Ensure the vendor understands their liability if a data breach occurs on their side. Your HIPAA IT compliance strategy depends on holding these vendors accountable for their security promises through formal, signed documentation that explicitly mentions your practice name.
One of the biggest risks involves how long a vendor stores the audio clips used to generate the charts. Some vendors delete the audio immediately after the text generation is finished, while others retain it for quality control or model improvement. For the highest level of security, prioritize vendors that minimize the storage duration of raw audio files, as these are primary targets for hackers.
Ask the vendor for a written policy on data destruction. You want to know exactly how and when they purge your files from their servers. If you are handling healthcare cybersecurity in-house, ensure you have a log of which patient encounters were processed through the tool and verify the vendor audit logs match your internal practice records.
Default settings in most software platforms are rarely the most secure. You must adjust the configuration to prevent the system from collecting unnecessary information. Many tools allow you to opt out of data sharing for research or product improvement. Disable these features immediately to ensure that your patient data is never used to train third-party algorithms that you do not control.
Assign a dedicated staff member to manage user permissions for the documentation software. Access should be restricted only to those who need the information to perform their roles, such as the doctor or dentist and clinical staff. Periodically review these permissions to remove access for employees who have left the practice or changed departments, as part of your it compliance checklist.
Begin by auditing your current clinical workflow to identify where documentation gaps exist. Create a formal list of requirements for any documentation vendor, prioritizing those that offer signed BAAs and transparent data retention policies. Once you select a vendor, perform a security assessment of their platform before full integration. Finally, train your clinical staff on the specific patient notification procedures required by your practice to maintain transparency during the visit.
We help practices in Los Angeles ensure their digital tools meet federal mandates. If you need assistance verifying a vendor or setting up secure configurations, contact our team for a cybersecurity audit to verify that your new tools align with your current security posture.
Sarah Mendez
HIPAA Compliance Lead
Sarah is part of the Titan Healthcare IT team, helping medical, dental, and clinic practices across Los Angeles keep their technology secure, compliant, and dependable. Connect with us on our contact page.
FREQUENTLY ASKED

Learn how common marketing tools like tracking pixels on your medical website can lead to HIPAA violations and discover how to audit your site to protect patient data today.
The one document regulators ask for first is the one most Los Angeles practices put off the longest. Here is what a real risk assessment includes, and what it should cost.
Most practices send PHI by email every day without realizing it. Here is how to make email safe, practical, and compliant without making staff hate it.
FREE IT RISK ASSESSMENT
Get a free, no-obligation IT risk assessment for your healthcare practice, we’ll identify HIPAA, security, and downtime risks and respond within 1 business hour. Only your name, email & phone are required.