Cybersecurity November 16, 2026 5 min read

Passwordless Authentication Healthcare: Faster Logins for Clinics

Streamline your clinical workflow by implementing passwordless authentication healthcare solutions. Protect patient data while reducing the frustration of repeated credential entry for your doctors and front desk staff.

DC

David Chen

Cybersecurity Director

Passwordless Authentication Healthcare: Faster Logins for Clinics

Defining Passwordless Authentication for Medical Practices

Passwordless authentication healthcare strategies replace traditional, manually typed credentials with cryptographic keys stored on a user device. Instead of asking a staff member to type a complex string of characters every time they sit down at a workstation, the system verifies their identity through hardware like a smartphone, an authenticator app, or a FIDO2 compliant security key. This method removes the risk of common human errors, such as password reuse or sticky notes with credentials left on a monitor, which are significant liabilities in any clinical environment.

Transitioning to these systems allows your team to focus on the patient instead of managing account lockouts. Because the security is anchored to a physical device in the staff member's possession, it creates a robust barrier against remote credential theft. When integrated with our healthcare cybersecurity protocols, this approach ensures that access remains limited to authorized personnel while significantly reducing the overhead associated with password resets. It provides a technical solution that keeps the focus on patient care rather than constant authentication friction.

  • Eliminates reliance on easily stolen passwords
  • Reduces time spent on credential management
  • Strengthens compliance with NIST guidelines
  • Allows for biometric device integration

How Passkeys Transform Clinical Workflow Efficiency

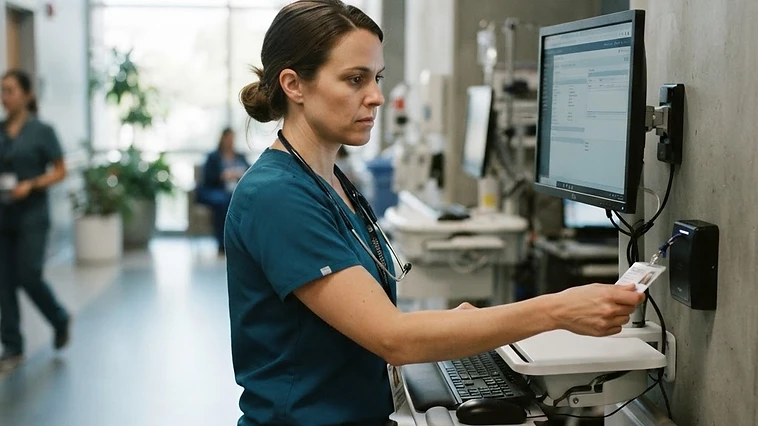
In a busy operatory or exam room, every second spent logging into an Electronic Health Record system impacts the patient experience. Traditional passwords force clinicians to stop what they are doing to type long, complex phrases, often while wearing gloves or assisting a patient. By adopting passkeys, the clinician simply taps a button on their mobile device or touches a fingerprint scanner to gain access. This creates a seamless flow that helps staff stay focused during examinations, consultations, and the documentation process without sacrificing essential data protection.

Clinical efficiency relies on tools that work with the provider, not against them. If you are struggling with outdated login procedures, our healthcare IT consulting team can assess your current environment to identify where passwordless adoption will provide the most benefit. We emphasize tools that integrate with existing hardware, ensuring that doctors and dental hygienists do not need to carry extra equipment while moving between rooms. This strategy stabilizes your workflow and prevents the common urge to share accounts, which is a frequent HIPAA violation.

  • Reduces login times in the exam room
  • Supports faster transitions between workstations
  • Minimizes the temptation to share passwords
  • Integrates with mobile clinical devices

Balancing Convenience and Strict Administrative Security

While clinical workstations should prioritize ease of access for providers, administrative accounts require a different security posture. Accounts with access to high-value data, such as billing records, payroll, or IT management consoles, should still utilize multi-factor authentication that includes hardware-bound tokens. This ensures that even if a staff device is lost or compromised, the most sensitive parts of your IT compliance infrastructure remain locked behind an additional layer of non-biometric verification. You should manage these accounts separately from the daily login accounts used by nursing or front desk staff.

Administrative staff are primary targets for phishing and credential harvesting. By keeping administrative passwords distinct and protected by hardware security keys, you limit the damage of a single compromised device. Our team helps you define which roles need simple passwordless sign-in and which roles require the maximum security provided by physical security keys. We structure these permissions to balance day-to-day usability with the robust defenses required by HHS regulations, ensuring that your practice remains secure while maintaining high levels of operational productivity across all departments.

  • Separates clinical access from administrative systems
  • Uses hardware keys for high-privilege access
  • Reduces exposure for sensitive billing data
  • Standardizes access control policies

Aligning Passwordless Access with HIPAA Requirements

The HIPAA Security Rule mandates that practices must implement procedures to guard against, detect, and report malicious software and unauthorized access. Passwordless authentication satisfies many of these requirements by providing strong, verified access control that exceeds traditional methods. Unlike a password that can be intercepted, a passkey is tied to a specific device and requires physical presence to activate. This effectively creates a unique digital footprint for every interaction, making it significantly easier to audit who accessed patient records and exactly when that access occurred.

Adopting these tools is a proactive step toward building a more defensible network. When an auditor asks how you manage user authentication, being able to demonstrate a move toward passwordless technology shows a clear commitment to modern network security management. This strategy removes the weak link of human memory and replaces it with cryptographically verifiable identity. It turns your login process into a central part of your compliance framework, ensuring your practice meets the high bar set by federal data protection standards.

  • Provides an audit trail for user access
  • Prevents unauthorized remote credential usage
  • Meets stringent HHS security mandates
  • Simplifies user identity verification

What to do next

Begin by conducting an inventory of your current login requirements across all departments, from the front desk to the billing office. Identify the roles where password fatigue is highest and prioritize them for a pilot program. Next, ensure your hardware is ready for modern authentication protocols and verify that your software vendors support FIDO2 standards. Finally, work with a professional team to configure the policies, train your staff on the new procedure, and monitor the results. Taking these steps in order will ensure a smooth transition with minimal disruption.

If you are ready to modernize your access controls and reduce administrative burden, reach out to our team. We specialize in implementing solutions that protect your practice while helping your staff work more efficiently. Whether you need an initial cybersecurity audit or a complete overhaul of your practice systems, we are here to support your goals. Visit our locations page to find the office nearest you or contact us today to start the conversation about improving your practice security.

  • Audit existing credential workflows
  • Pilot passwordless tools in one department
  • Update practice cybersecurity policies
  • Train staff on new login procedures

Key Takeaways

  • 1Passwordless authentication uses device-bound keys to replace insecure passwords.
  • 2Clinical workflows benefit from faster logins without sacrificing HIPAA compliance.
  • 3Keep high-privilege administrative accounts behind additional hardware-based security keys.
passwordless authentication healthcaresecure clinical loginsHIPAA compliant ITmedical practice cybersecuritypasskeys for doctors
DC

David Chen

Cybersecurity Director

David is part of the Titan Healthcare IT team, helping medical, dental, and clinic practices across Los Angeles keep their technology secure, compliant, and dependable. Connect with us on our contact page.

FREQUENTLY ASKED

Cybersecurity FAQ

Yes. Passwords can be phished, guessed, or stolen from databases. Passwordless authentication uses cryptographic keys stored on a secure physical device, meaning a hacker would need both your specific physical device and your biometric data or PIN to gain access to your account.

Related Articles

All articles
Telehealth Security: HIPAA Compliance for Virtual Care
Cybersecurity
5 min

Telehealth Security: HIPAA Compliance for Virtual Care

Secure your practice virtual visits by implementing strict patient identity verification and encrypted communication channels. Learn how to maintain HIPAA standards during every remote consultation to protect sensitive health data.

David Chen · Cybersecurity DirectorRead

FREE IT RISK ASSESSMENT

Find Your IT Risks Before They Find You

Get a free, no-obligation IT risk assessment for your healthcare practice, we’ll identify HIPAA, security, and downtime risks and respond within 1 business hour. Only your name, email & phone are required.

Services Interested In *

No obligation · Your details are never shared